Assistive Technology
What Happens to Your Data in a Learning or Therapy App?
Follow the actual activity and ask how its information is collected, used, shared and retained.
Archive edition: 16 September 2026 · assigned for archive organisation
On this page
- At a glance
- Map the actual activity
- Read more than the store label
- Check permissions in context
- Follow the information beyond capture
- Clarify sharing and account roles
- Separate a recommendation from organizational approval
- Plan for ending use before it becomes urgent
- A practical example
- Common questions
- Sources and scope
A learning or therapy app may handle more than the information typed into a visible form. Depending on the service and settings, questions can arise about recordings, uploaded documents, account details, usage information and material shared with other people. A useful privacy review follows the actual task and asks where each kind of information goes.
This guide provides questions for families, adult users, schools and service providers. It does not assess a named app’s compliance or determine which privacy law applies to an individual situation. A store listing, recommendation or paid subscription is not enough on its own to answer the questions below.
Map the actual activity
Begin with a plain-language description: “record a reading practice,” “upload a worksheet” or “share a communication page with a support worker.” List the information involved, including details about other people who may appear in recordings, images or documents.
Ask which steps are necessary and which are optional. Could the task be tried with a fictional example or a short non-sensitive sample? Does the app require an account for the desired feature, and is a school-managed account different from a personal one?
A general promise of personalization is not a complete explanation. Ask what information produces the personalization, whether it can be turned off and what changes if the user declines. Record the answer for the actual account and feature rather than assuming every version of the service works identically.
Read more than the store label
Apple’s explanation of App Store privacy information states that developers report the information and that disclosures can cover different uses or versions of an app. The policy may provide more detail about those differences. Treat a label as a useful starting point, not a complete independent audit of the service.
Google Play’s Data safety explanation similarly describes developer disclosures covering app versions, with practices potentially varying by use, region and age. It also explains that its collection and sharing categories have defined exceptions. A short label therefore should not be read as a universal statement that information never leaves the device.
Locate the current privacy policy and identify which organization provides the service. Look for information specific to children, school accounts, clinical use or the particular feature when relevant. If a policy is unclear, ask a focused question rather than filling the gap with an assumption.
Check permissions in context
The Office of the Privacy Commissioner of Canada’s mobile-app guidance advises comparing requested permissions with the policy and the app’s purpose. This longstanding resource, dated 2014, supplies general questions; it is not a current walkthrough of every operating system’s permission controls.
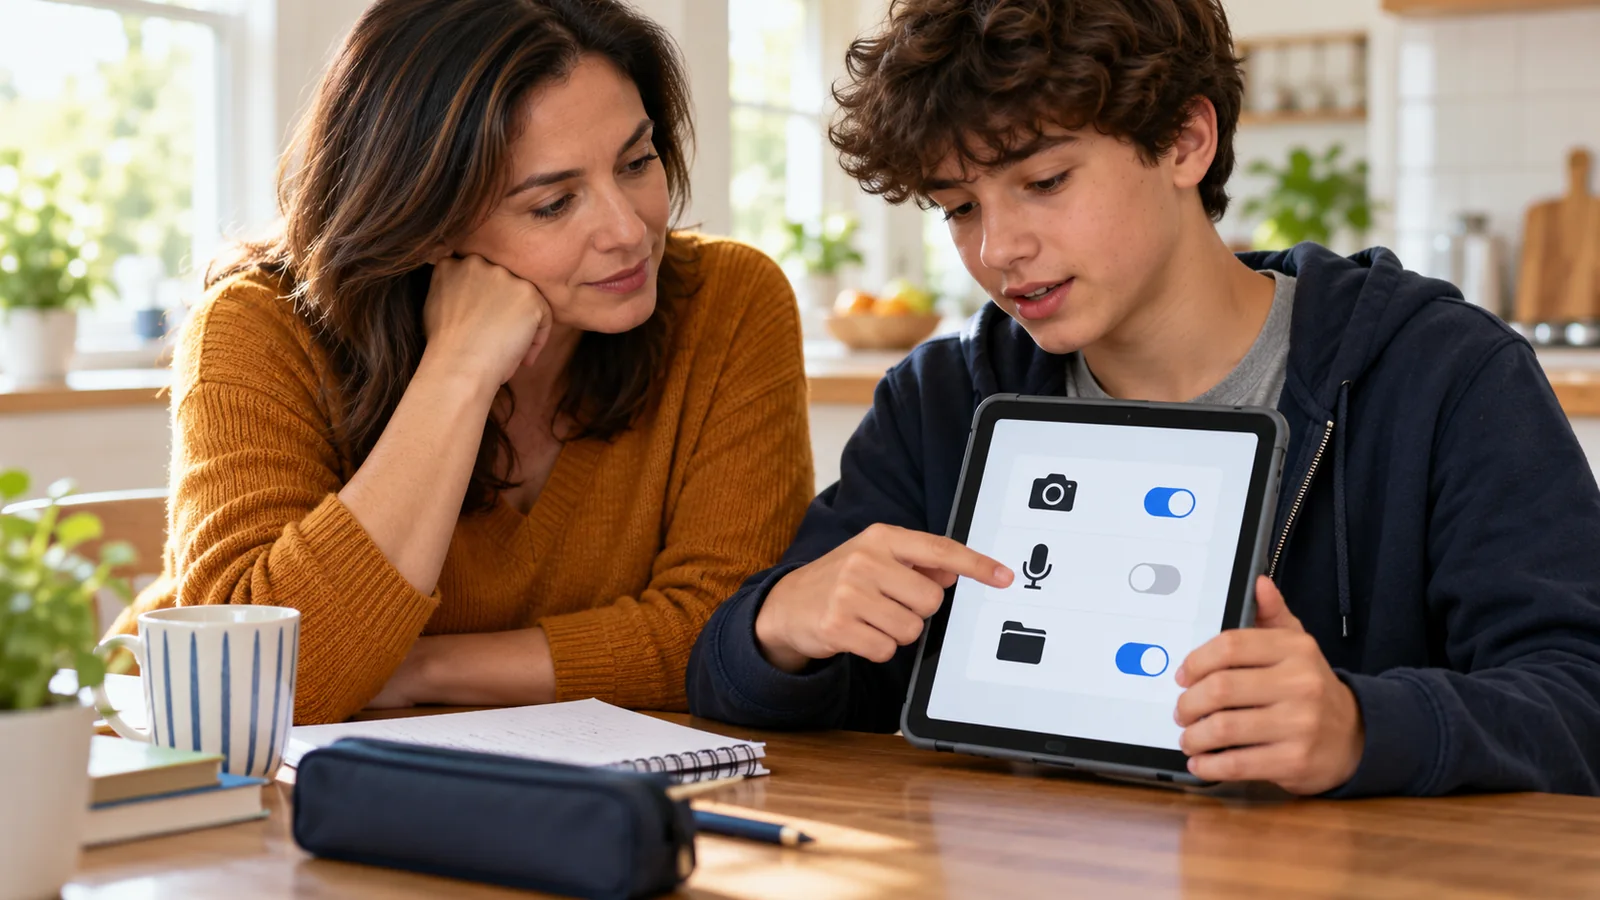
For a reading task, microphone access may have an understandable function if the app records speech. Ask whether recording is optional, when the microphone is active and what happens to the result. The presence of a permission request does not explain storage, reuse or who can listen later.
Review camera, photo, file, location and contact access in the same task-based way. Use the actual device’s available choices and check what remains usable when optional access is declined. Do not disable an essential access method without discussing a workable alternative with the person.
Follow the information beyond capture
| Stage | Question | Information to request |
|---|---|---|
| Collection | What is recorded or uploaded for this feature? | Required and optional data types |
| Processing | Does processing occur on the device or through a service? | The actual feature’s data flow |
| Access | Who can see the content and account activity? | User roles, administrators and other recipients |
| Reuse | Is content used for analytics, advertising or model improvement? | Purpose, controls and applicable terms |
| Retention | How long are content and associated records kept? | Retention rules and relevant exceptions |
| Leaving | How can useful work be exported and deletion requested? | Format, process and confirmation |
These are questions to investigate, not statements that every app performs every listed activity. Record answers as confirmed, unclear or not applicable. An unanswered question should remain visible in the decision rather than being silently treated as reassuring.
Clarify sharing and account roles
Ask who owns or administers the account and who may change permissions. A teacher, clinician, parent, support worker and adult user may have different roles. Clarify which person can invite others, download content or remove access when a relationship changes.
Review the actual sharing controls before adding identifiable information. A link intended for one supporter may have a broader access setting than expected. Use a harmless sample to understand the workflow, and ask the organization to explain managed settings that the user cannot inspect.
Include the person whose information is involved in an accessible conversation about the arrangement. Explain what will be recorded, who is expected to see it and how they can raise a concern. A helper’s convenience should not replace the person’s understanding and appropriate participation.
Separate a recommendation from organizational approval
If a school or service asks someone to use an app, ask which account and features have been approved and who can answer privacy questions. A staff member’s informal recommendation may not describe the organization’s full review or permitted data use.
Ask what alternative is available if the proposed feature requires information the person does not wish to provide or if an access barrier prevents use. The answer may involve a different workflow, another tool or an organizational decision. Do not assume the family or user must solve every concern alone.
For therapy-related records or other sensitive content, clarify the responsible service’s process before uploading. This guide cannot decide whether consent, another authority or a particular contract is sufficient in that setting. Obtain a specific answer from the appropriate privacy contact where needed.
Plan for ending use before it becomes urgent
Ask how to retain useful work in an accessible format and test an export with sample material. A file that downloads successfully may still omit recordings, symbols or structure the person relies on. Check the result in the intended destination.
Distinguish uninstalling an app, cancelling a subscription, closing an account and requesting deletion of stored information. Do not assume one action completes the others. Read the service’s current instructions and ask about records that may remain and the reasons given.
For a school-managed or clinical account, coordinate with the responsible organization before removing material that must be retained or belongs to someone else. Keep a record of the request and response without making unnecessary additional copies of sensitive information.
- Map: identify the task, information and people involved.
- Ask: compare policies, disclosures, permissions and specific answers.
- Decide: choose a workable arrangement and a review point.
A practical example
In this fictional example, a family is considering an app that records reading practice. They first test it with a short invented passage and ask whether recordings stay on the device, who can access them and how they can be deleted.
The school clarifies which account arrangement it supports and which sharing feature should be used. One question about retention remains unresolved, so the family keeps using the existing reading routine while the appropriate contact obtains an answer.
The review is focused on the actual activity. It does not depend on assuming that every app is unsafe or that a store label answers every question.
Common questions
Does a store privacy label certify an app as safe?
No. Read it as a disclosure with a defined scope, alongside the policy and information about the actual account and feature.
Does a paid app automatically provide stronger privacy?
Do not assume so. Compare its stated practices and controls rather than using price as a privacy guarantee.
Is microphone permission the same as permission to store recordings?
No. Ask separately about capture, storage, access, reuse and retention for the feature being used.
Should I upload real records during a first trial?
Use a non-sensitive sample where possible while confirming the appropriate account, permissions and data-handling arrangements.
Can a school account differ from a personal account?
Yes, arrangements may differ. Ask which version, features and managed settings apply instead of generalizing from another account.
What if the privacy policy is difficult to understand?
Ask the provider or responsible organization a specific question about the task and information involved. Keep unresolved points visible.
Does uninstalling remove all service-held information?
Do not assume it does. Check the separate account and deletion process and ask what may remain.
Should the person using the app be included?
Yes. Use an accessible explanation and involve them in choices about their information, preferences and concerns.
Who answers questions about a required school app?
Ask the school to identify the responsible administrator or privacy contact and explain the approved account and workflow.
When should we review the arrangement again?
Review when features, policies, accounts, sharing roles or the task change, and before transferring or closing an account.
Sources and scope
Apple and Google describe their store-disclosure systems. The OPC’s 2014 resource supports general permission and policy questions, not current interface instructions. No named app was audited or declared compliant.
- Apple: App Store privacy information — developer disclosures and scope.
- Google Play: Data safety information — categories, variation and exceptions.
- OPC: Your privacy and mobile apps — general policy and permission questions.